All news
External Scanning: Verifying Actual Internet Accessibility of Resources
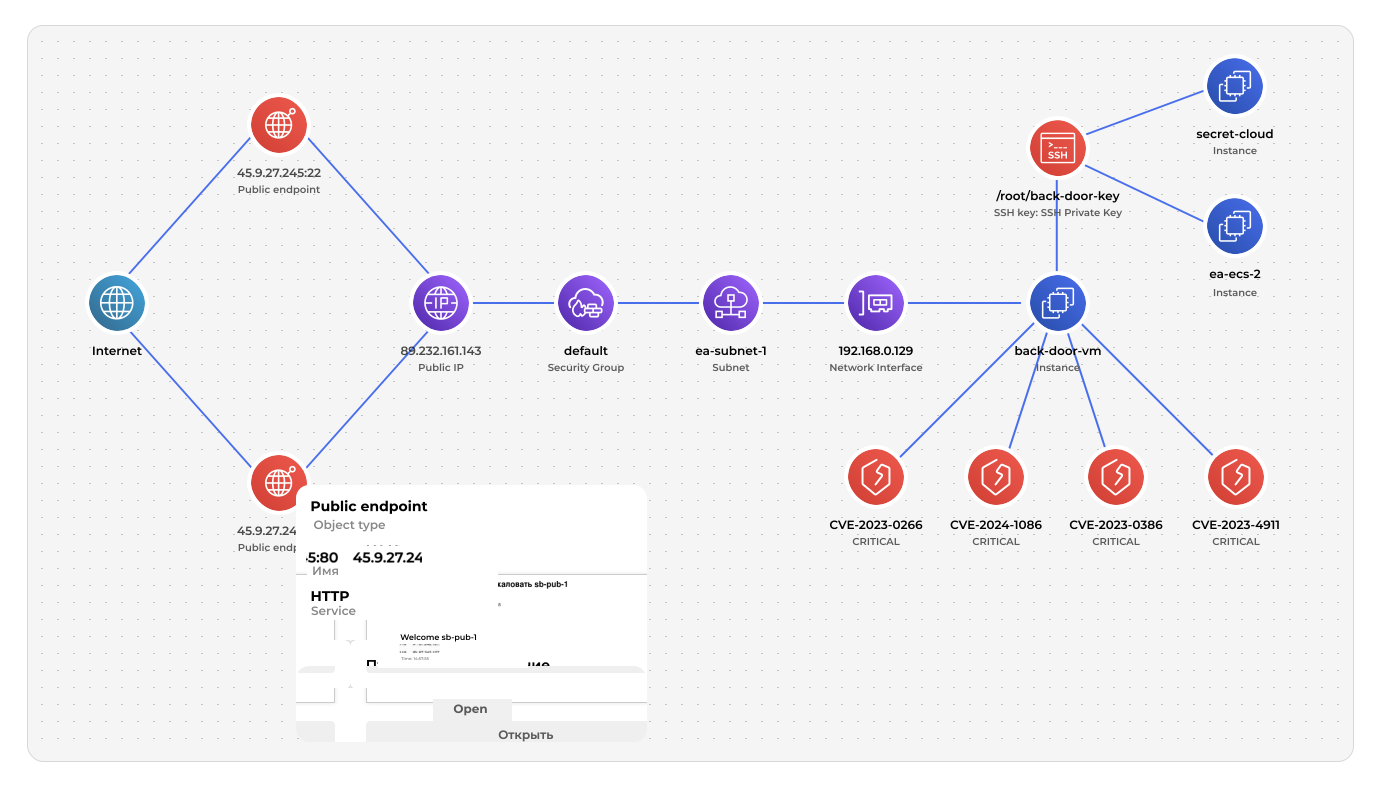
The CSPM module in Cloud Advisor analyzes the entire network connectivity chain - including load balancers, NAT, public IP addresses, security groups, and other objects - to determine which resources are accessible from a wide range of external IP addresses. Now, to further verify public accessibility, the platform also performs external scanning: it connects to potentially open ports from outside and checks their actual status - whether the port is open or closed. This allows Cloud Advisor to identify publicly exposed applications - combinations of an IP address and an open port through which applications are accessible from the internet. Each publicly exposed application detected during external scanning is saved in the resource properties and taken into account when building Attack Paths. This makes externally verified accessibility another criterion for context-based threat prioritization. In addition, external scanning reduces false positives. The security team gets not only a public accessibility assessment based on cloud configuration, but also external confirmation in the form of a service response or screenshot. External scanning is enabled by default. You can disable it in the Cloud Advisor web console: “Settings” → “Scan” → “External Scanning”.